Beast Ransomware Uses GUI-Based Encryption, Network Discovery and Recovery Evasion Techniques
 Hari
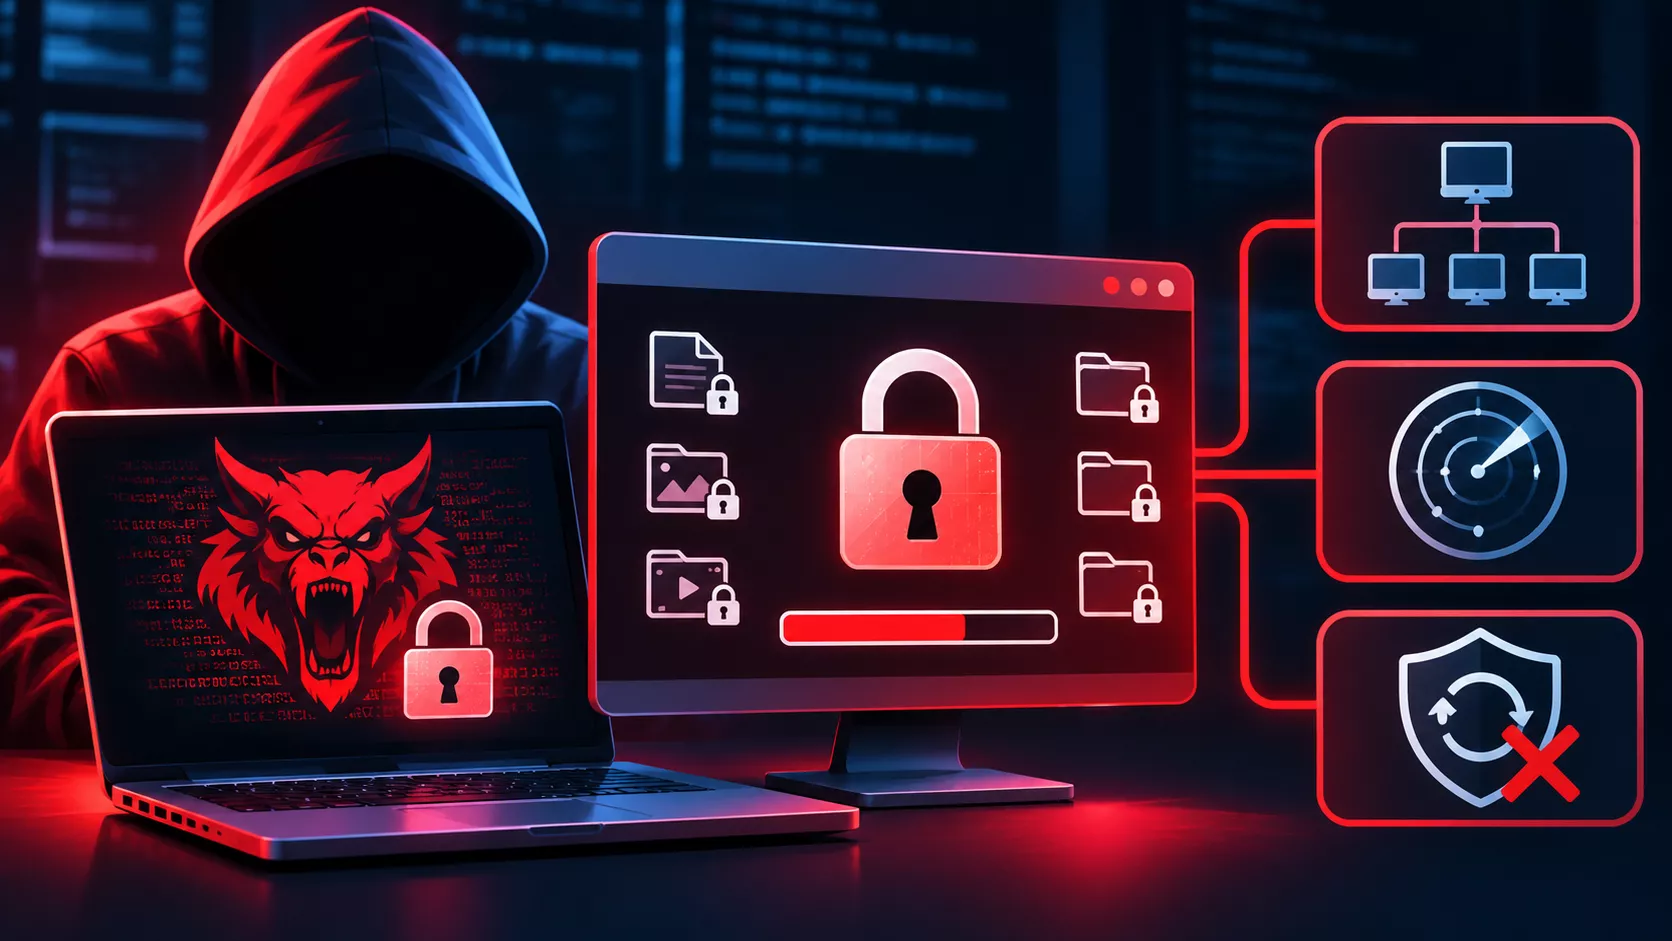
AttackIQ has published a technical teardown of Beast, a Ransomware-as-a-Service family that surfaced on the RAMP forum in June 2024 and is reportedly the successor to Monster ransomware. Symantec and Carbon Black attribute both to the actor Hyadina, and Symantec linked the operation to GodDamn Ransomware in July 2026.
Beast’s builder generates payloads for Windows, NAS appliances and VMware ESXi, a hypervisor-focused approach also seen in the GhostFrame ESXi implant tied to Settra ransomware. The analyzed sample is an 81 KB 32-bit C/C++ PE that decodes stack-built strings with a single-byte XOR key of 0x55.
Beast Ransomware
Beast’s distinguishing feature is an operator GUI, opened by pressing ALT+CTRL and typing 666. Affiliates enumerate logical drives, shares and subnets, select targets, then start, pause, resume or stop encryption while watching progress.
Behavior is also tunable through flags such as -K for process and service termination, -N for network discovery and -S for shadow copy deletion. Defaults come from a ChaCha20-encrypted blob in the .data section, with the key and nonce stored directly before it, so the configuration can be recovered statically.
Lateral discovery starts from the ARP cache. GetIpNetTable returns neighbors, which are filtered to 10., 172., 192.168. and 169. ranges and reduced to unique /24 subnets.
Those are probed asynchronously over TCP/445 using an I/O completion port, and responding hosts have their shares enumerated through NetShareEnum, WNetOpenEnumW and WNetEnumResourceW, with ADMIN$ excluded.
The queued UNC paths overlap with the SMB-centric propagation seen when the SCKit worm abused ScreenConnect RMM to hijack 288 endpoints. Beast also mounts unmounted volumes through SetVolumeMountPointW and enables SeTakeOwnershipPrivilege via AdjustTokenPrivileges.
Recovery inhibition is thorough. Beast terminates 52 processes and stops 73 services, including Veeam, Acronis, Backup Exec and SQL Server components, using the Service Control Manager and EnumDependentServicesW to stop dependents first.
Locked files are released through Restart Manager (RmStartSession, RmRegisterResources, RmGetList, RmShutdown). Shadow copies are removed by querying Win32_ShadowCopy through IWbemServices::ExecQuery and calling DeleteInstance, after an administrative check.
SHEmptyRecycleBin finishes the cleanup. A geographic kill-switch skips CIS and other listed locales, checked with GetSystemDefaultUILanguage and GetLocaleInfoW.
Persistence uses an HKCU Run key named after the victim GUID, and the -I flag relocates the binary to %ALLUSERSPROFILE% under an eight-letter random filename. A BEAST HERE? mutex enforces single execution. A beacon to iplogger[.]co sends the victim ID in the User-Agent and BEGIN or END in the Referer, bracketing the encryption window.
The cryptography combines ChaCha20 with a Curve25519 ECDH hierarchy. Each machine gets a session keypair whose private half is wrapped under two attacker public keys. Each file then gets an ephemeral keypair, with the shared secret hashed through SHA-512 into a unique key and nonce.
A 160-byte footer ending in the marker 66 6B EA 57 1A BE 16 66 prevents double encryption. Intermittent encryption processes 128 KiB chunks at 25%, with a three-chunk minimum. Files of 1 GiB or more get alternating chunks from the start, capped at 4096 chunks, or 512 MiB.
Defenders should hunt for WMI shadow copy deletion, Restart Manager calls from unsigned binaries, bursts of TCP/445 connections, and default.key files beside executables. Identity-layer abuse of the kind in the Citrus ransomware intrusion chain shows why detections should cover the full kill chain rather than the encryption stage alone.
Site: Thecyberdef.com
Follow TheCyberDef on Google News, LinkedIn & X for the latest cybersecurity updates. Stay informed.
About the Author

 Kiran