Kiran
A sprawling network of over 1.7 million Chinese-language gambling domains is quietly serving as the connective tissue for money laundering, consumer fraud, and, in a smaller but far more alarming subset, nation-state espionage, according to new Infoblox Threat Intel research.
The report identifies three visually indistinguishable categories of malicious casino sites that behave completely differently underneath. Type 1 covers over 1.7 million legitimate-feeling illegal Chinese-language gambling sites that facilitate real betting and function as a laundering pipeline out of China and North Korea’s cybercrime proceeds.
Type 2, dubbed “scambling,” comprises thousands of rigged gambling sites a term popularized by journalist Brian Krebs in 2025 that lure victims with inflated deposit bonuses before blocking withdrawals entirely.
China-Linked PeckBirdy APT Uses Fake Casino Sites
Type 3 is the smallest but most dangerous: dozens of decoy casino and adult-content domains operated since 2023 by a China-aligned APT group using a command-and-control framework Infoblox calls PeckBirdy, targeting corporate and government networks across Asia.
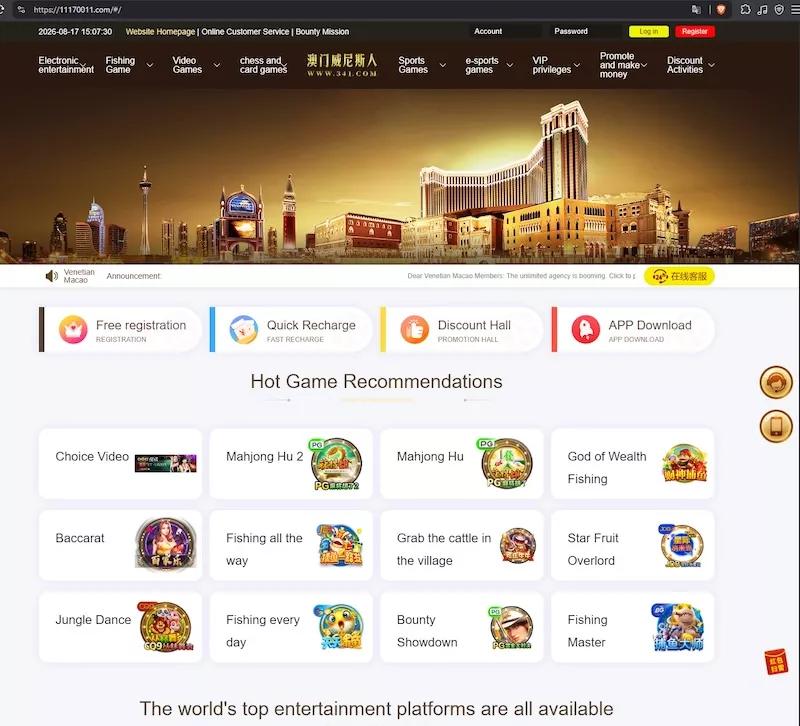
Researchers traced PeckBirdy activity to a decoy domain, vip311[.]cc, hosting KY-branded casino content that secretly loaded a malicious script from cache-mcp[.]com, which in turn pointed to a WebSocket C2 endpoint, mcp-source[.]online.
That second-stage domain had zero detections on VirusTotal as of late August 2026, despite being an active espionage channel a gap Infoblox says reflects how poorly automated scanners capture WebSocket-based C2 traffic hidden behind casino front-ends.
A related domain, cache-cdn[.]org, previously flagged by Trend Micro in January 2026, had only 13 detections.
“The industry’s blind spot isn’t a lack of visibility it’s a lack of curiosity. Every SOC analyst has seen a gambling or adult-site alert and closed it as ‘user browsing violation’ without a second thought. PeckBirdy’s operators are counting on exactly that reflex, and until triage playbooks treat casino domains as a category worth interrogating rather than dismissing, this decoy model will keep working.”
Infoblox’s telemetry shows just over 3% of enterprise customers resolved at least one PeckBirdy C2 domain, with education, IT, banking, and government among the top targeted sectors consistent with a documented 2024 attack on a Philippines education institution.
Crucially, the count of distinct C2 domains queried matters more than raw query volume: hitting three to ten unique PeckBirdy domains is a stronger compromise signal than repeatedly resolving a single one.
Infrastructure analysis reveals a “fronting” pattern across roughly 967,000 Chinese-language casino domains registered through U.S. registrars but hosted on Chinese or Hong Kong infrastructure, putting them nominally under U.S. abuse-reporting jurisdiction while operationally shielded overseas.
Major U.S. cloud providers, including Amazon, Microsoft, and Cloudflare, continue to unknowingly host segments of this ecosystem, likely via account theft techniques known as “infrastructure laundering”.
Infoblox urges defenders to stop auto-closing casino and adult-domain alerts as policy violations, instead checking for payload behavior before dismissal.
The report also references a July 2026 UNODC assessment estimating illegal betting revenue at up to $1.7 trillion annually and scam-related losses across East and Southeast Asia reaching $88.3–$114.1 billion in 2025 alone, nearly triple 2023 figures.
With domain-blocking efforts, like the Philippines’ 2024 takedown of over 7,000 sites, proving largely ineffective against rapidly rotating infrastructure, UNODC and Infoblox both frame this as a systemic detection failure rather than a one-off campaign.
Site: Thecyberdef.com
Follow TheCyberDef on Google News, LinkedIn & X for the latest cybersecurity updates. Stay informed.
About the Author

 George antony