Exposed Attacker Server Reveals MSSQL Intrusion Tied to Viva Aerobus, Toolkit and Loot Leaked
 Kiran
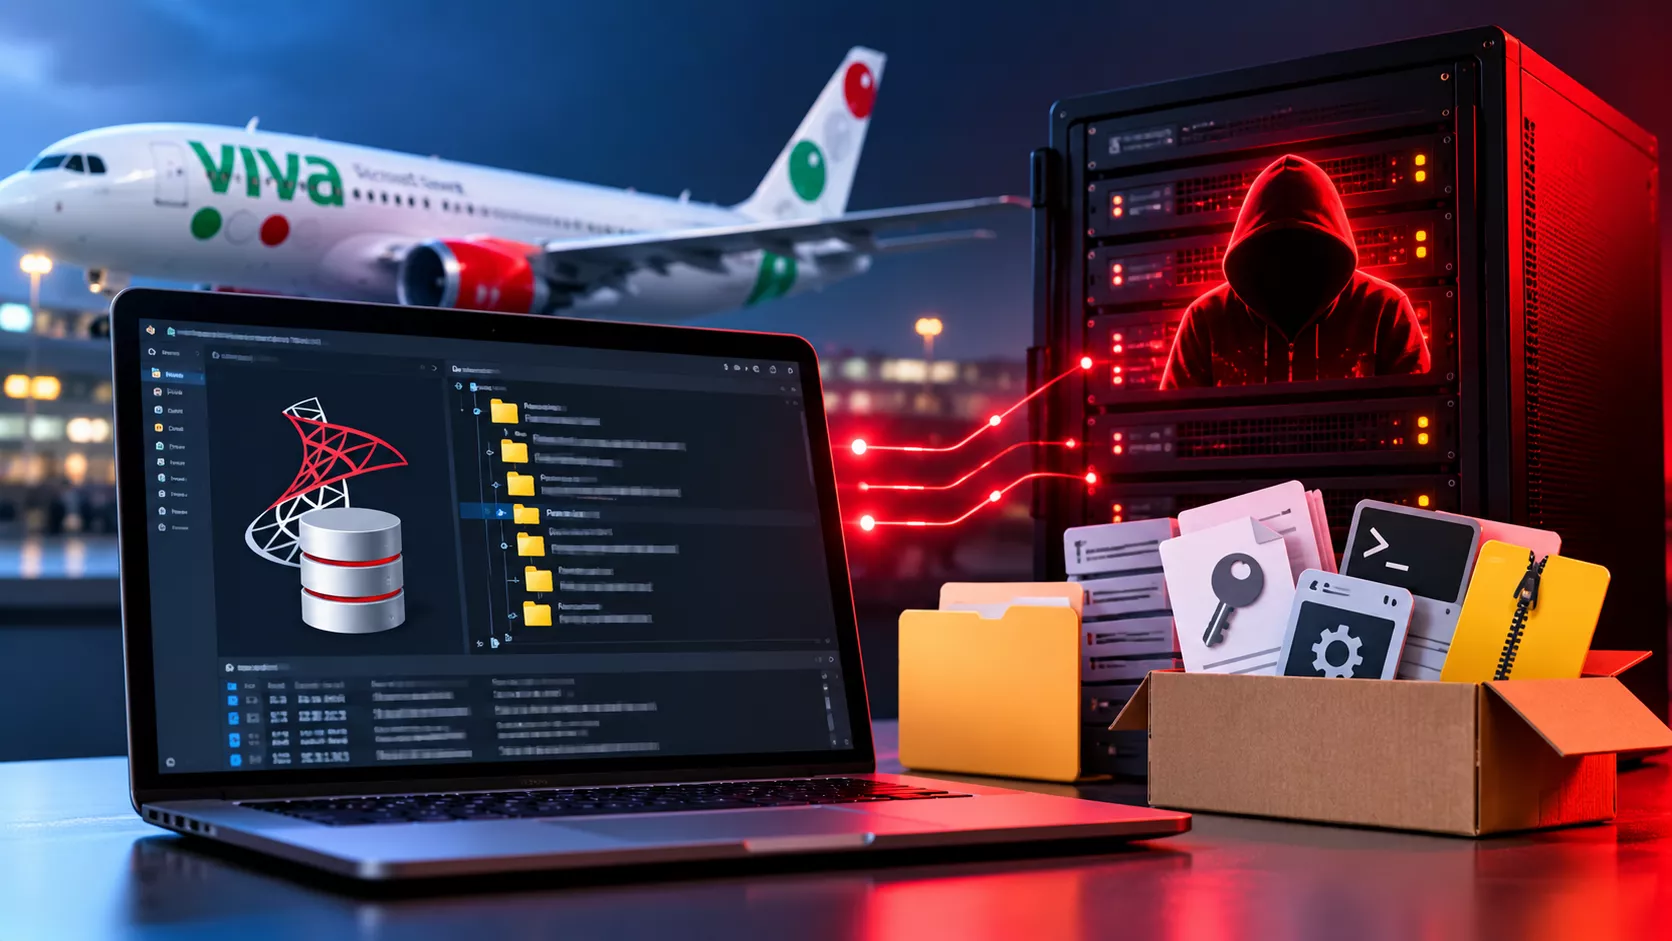
An attacker’s unprotected staging server gave defenders a rare view of an MSSQL-focused intrusion tied to a Viva Aerobus-side environment. It also exposed the stolen material to anyone who found it.
On September 25, 2026, an attacker-controlled server at 151.243.232.123 sat on the public internet with no authentication. It held tools and stolen files. At 16:20, a victim-side Microsoft SQL Server pulled a payload from it.
Within minutes, an unrelated external host began enumerating its directories. ThreatMon’s Threat Intelligence Team found the infrastructure during routine threat hunting. The activity ran between September 25 and 29.
Exposed Attacker Server Reveals MSSQL Intrusion Tied
ThreatMon found no confirmed lateral movement and no confirmed theft of passenger, payment, or other sensitive business data.
The HTTP server hosted tools, received collected files, and supported post-exploitation work. Nothing separated its working directories from the internet.
Recovered logs, tooling, credential output, and SQL Server Management Studio (SSMS) artifacts let researchers rebuild the workflow. It began with MSSQL command execution and moved to credential harvesting.
It then collected configuration and source code and prepared credential reuse against other systems. The evidence supports these stages, but it does not confirm access to additional systems.
The server held 17 named tools. They included chrome_dump.ps1 and cred_dump.ps1 for browser and Windows credential theft, and cred_enum.ps1 for enumeration. sqlspray.ps1 and mssqltest.ps1 tested SQL credentials. exfil.py and upload.py moved files, and vault.cmd and vtest.ps1 likely targeted Windows Credential Manager. The loot/ and loot2/ directories also held cred_dec.txt, mdump.txt and httpd.log.
The attacker relied on xp_cmdshell, which runs operating-system commands when enabled. The tooling submitted Windows commands and Base64-encoded PowerShell through an MSSQL session.
It also moved data through the same channel. A file could be read, split into chunks, Base64-encoded, and returned in query output, so no conventional command-and-control channel was needed.
The most revealing artifact was SSMS user-settings data. It contained server references, database usernames, and DPAPI-protected saved passwords, which together form a map of follow-on targets.
The attacker also gathered source code and configuration files that referenced SQL, OAuth, mail, SFTP, and payment or reporting integrations. Companion tooling tested SQL logins, checked server-role membership, and probed SMB administrative shares.
- 16:20: The victim-side MSSQL environment retrieved a payload.
- 16:21–16:23: An unrelated host enumerated the server and loot directories.
- 16:30: Self-test-style requests came from the staging host.
- 18:04–18:05: Additional external hosts fetched tools and loot artifacts.
The attacker’s delivery worked as intended. At the same time, the missing authentication opened a second exposure event on top of the original intrusion.
ThreatMon mapped the activity to eight MITRE ATT&CK techniques: T1059.001, T1059.003, T1003, T1555, T1552.001, T1021, T1074 and T1041. The public indicators are limited to attacker-side artifacts.
| Type | Indicator |
|---|---|
| IPv4 | 151.243.232.123 |
| SHA256 (exfil.py) | c38f49ba68b891bb476510704cddf080798f3c70075e2a517e98e04e833f64fa |
| SHA256 (upload.py) | 33aeaaa3d57b7785ef2be5b8ccd39d534b8af50e0cd32a5036fdb64601a52fc9 |
| SHA256 (sqlspray.ps1) | 8b6c53e3d57b4c3049f3d0765a44d9a52feb6af78f1eaa5aff19daf1b9665998 |
| Path | C:\Windows\Temp\artex |
Defenders should check historical network telemetry for the IP, then search endpoints for the hashes and the working path. Any unexpected xp_cmdshell use deserves immediate investigation.
That is especially true when cmd.exe or powershell.exe runs under a SQL Server service account. Treat SSMS metadata as sensitive. Assume any credential or secret that reached the exposed server is compromised, because the original operator was unlikely to be the only party with access.
The case shows both sides of leaky attacker infrastructure. It gives defenders rare insight into post-exploitation behavior, and it widens exposure of data already taken from the victim.
Site: Thecyberdef.com
Follow TheCyberDef on Google News, LinkedIn & X for the latest cybersecurity updates. Stay informed.
About the Author