Notion Fireworks AI Incident Exposes Chat Transcripts: What Affected Customers Must Do Now
 Hari
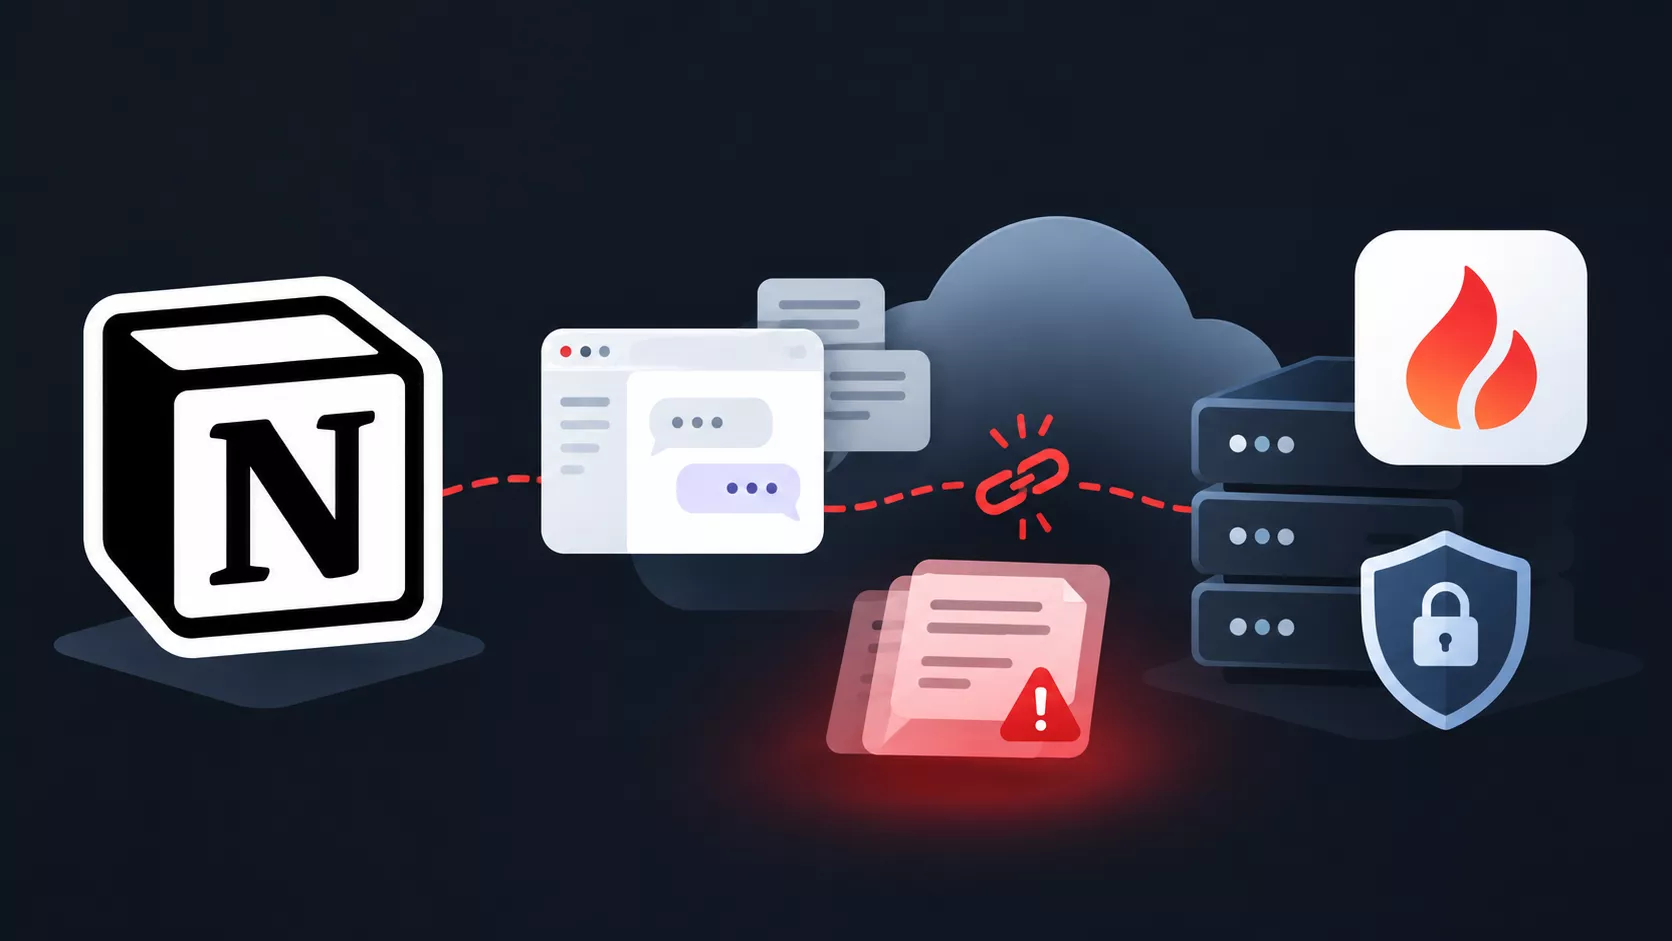
Notion has disclosed that a security incident at third-party AI infrastructure provider Fireworks AI may have exposed Notion AI chat transcripts tied to its Insights feature, affecting fewer than 1% of Notion workspaces.
The company says it has notified affected customers and is continuing to investigate, although it maintains that its own systems were not breached. Fireworks first notified Notion on the evening of November 2 that malicious actors had accessed a small set of data.
Notion’s initial review found that the dataset contained synthetic testing data rather than customer data, prompting the company to disconnect from Fireworks, delete data held in Fireworks systems, and halt communications between the two platforms by the morning of November 3.
Notion Fireworks AI Incident Exposes Chat Transcripts
The situation changed on November 6, when Fireworks told Notion that attackers may have accessed potential customer data. Notion launched a second investigation, and on November 8 Fireworks confirmed the final affected dataset. Notion then contacted impacted customers on November 9 and published a public security advisory.
Fireworks separately says its October 2026 incident involved unauthorized use of internal credentials and access to environment variables used in evaluation jobs across a limited number of customer accounts. Its security bulletin says it is actively monitoring the situation and has implemented security-hardening measures.
Notion says the newly identified dataset included Notion AI chat transcripts used by the Insights feature, which is designed to help organizations understand how their teams use AI. For the vast majority of affected workspaces, those transcripts were “unattributable”: they were not labeled with the author, workspace, or company, and did not include tool-call results.
That means, according to Notion, the exposed material may reveal the contents of individual AI chats but does not inherently link those chats to a particular user, workspace, or organization. The company says no other Notion features were affected.
Notion has disabled Insights while it investigates. Its support documentation now states that the feature is temporarily paused, with use-case and conversation-count information unavailable.
Fireworks AI is a widely used AI infrastructure platform serving tens of thousands of customers and hundreds of thousands of developers. Notion used the vendor for two purposes: classification jobs supporting Insights, and general inference for open-weight models served inside Notion’s product.
Following the incident, Notion says it no longer serves open-weight models through Fireworks. The company has also cut off data flows and removed data from Fireworks systems, reducing its immediate exposure while it evaluates the scope and consequences of the compromise.
Notion has emailed instructions allowing affected customers to retrieve and review the impacted data securely within their workspaces. It is advising them to treat the exposed transcripts as if they had been publicly exposed.
The most urgent technical concern is credential leakage. Notion recommends that customers who entered passwords, API keys, or other sensitive credentials into Notion AI during the relevant period rotate those secrets immediately.
Even if the transcripts were not directly attributable to a workspace, the contents themselves could include confidential internal information, proprietary material, or authentication details.
The episode highlights a growing supply-chain risk in enterprise AI: a company’s own infrastructure may remain uncompromised while a third-party model provider becomes the point of exposure.
Notion’s decision to disconnect, delete vendor-held data, and suspend the affected feature reflects a containment-first response, but the incident still leaves customers assessing what sensitive prompts or AI-generated content may have entered an external processing pipeline.
Notion says its investigation remains ongoing and that it will update its advisory as more information becomes available. Customers who have not received a notification have not been identified as affected and do not need to take action at this time.
Site: Thecyberdef.com
Follow TheCyberDef on Google News, LinkedIn & X for the latest cybersecurity updates. Stay informed.
About the Author